

What we do
Network
Our own routed network: carriers, peering, the datacenter fabric, encrypted links between sites and the discipline we change it with.
Network
How we build it.
Page by page.
Each page covers one capability: what it is, how we build it, what it protects you from and how it works for customers today.
- Authoritative DNS and reverse DNS, run as infrastructureAuthoritative DNS on PowerDNS: a hidden primary, dnsdist-protected secondaries in Athens and Toronto, DNSSEC, and a reverse record for every address we assign.
- Datacenter fabric: EVPN/VXLAN on Cisco NexusEvery EuroVPS host is dual-homed into a Cisco Nexus 9000 leaf and spine fabric with BGP EVPN, VXLAN and anycast gateways, checked against a signed baseline.
- How we change things: network change disciplineBackup before every change, one change at a time, one half of a redundant pair at a time, automatic rollback, verified live. How EuroVPS changes its network.
- IPv6, native and dual-stackNative dual-stack IPv6 in Athens, Amsterdam and Toronto, announced from our own address space down to your gateway. No tunnel, no proxy, no translation.
- Managed perimeter firewallsRedundant OPNsense firewall pairs with stateful failover, per-host default-deny rules, threat intelligence, country blocking and single-country access.
- Move to us without renumbering: Layer 2 extensionMove to EuroVPS without renumbering. We stretch your VLANs from your current site or between our datacenters, so servers keep their IPs and move one at a time.
- Multi-site encrypted backbone: the DMVPN meshAthens, Amsterdam and Toronto joined by a Cisco DMVPN mesh: AES-256 IPsec, BGP routing, redundant hubs in every datacenter, site-to-site networks for customers.
- Network monitoring and evidenceEvery EuroVPS router, switch, firewall and link is watched by Zabbix, Graylog and a RIPE Atlas anchor, and the data is kept so every question has an answer.
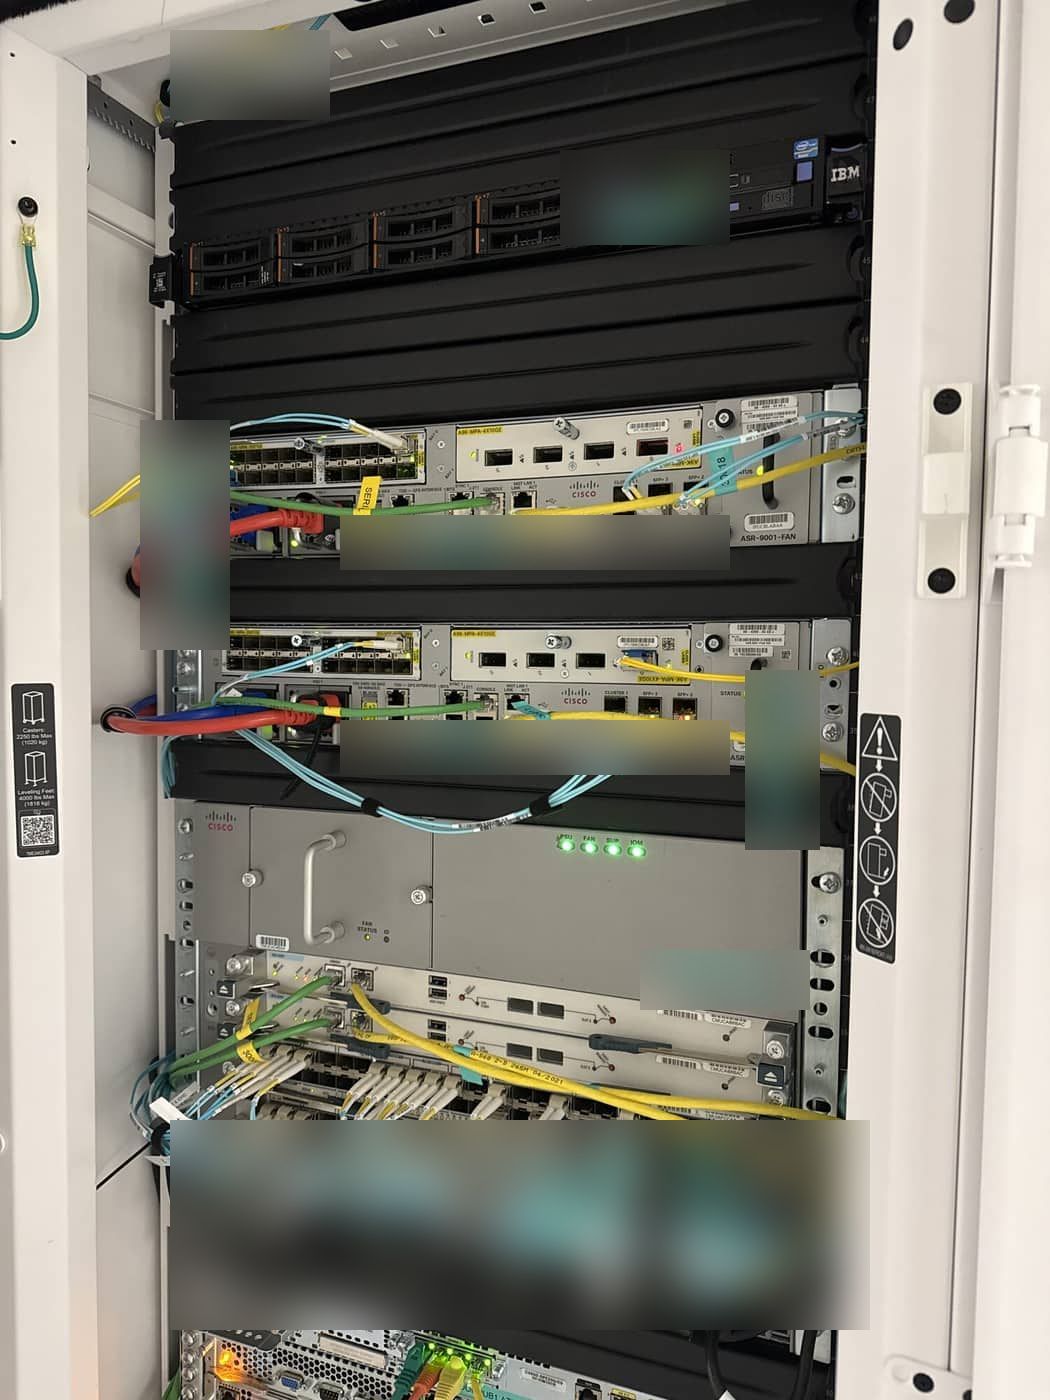
- Our own network: two ASNs, many carriers, peeringEuroVPS runs its own internet edge: two RIPE autonomous systems, Cisco ASR 9000 and Juniper MX204 routers, tier-one transit, direct peering at GR-IX and NetIX.
- Private connectivity: VPN gateways and leased linesDedicated OPNsense VPN gateways with per-user certificates, leased lines into our fabric and site-to-site hubs. Never a slot on a shared box.
Your next infrastructure partner
Let’s look at
your setup.
Tell us what you run today and what needs to improve. An engineer will review your brief and help you plan the next step.
+357 222 32280
who will look after your infrastructure.
Let’s start with your setup.
A little context helps us start the right conversation.