

What we do · Storage and compute
Managed backup on Veeam and Borg, pull-only
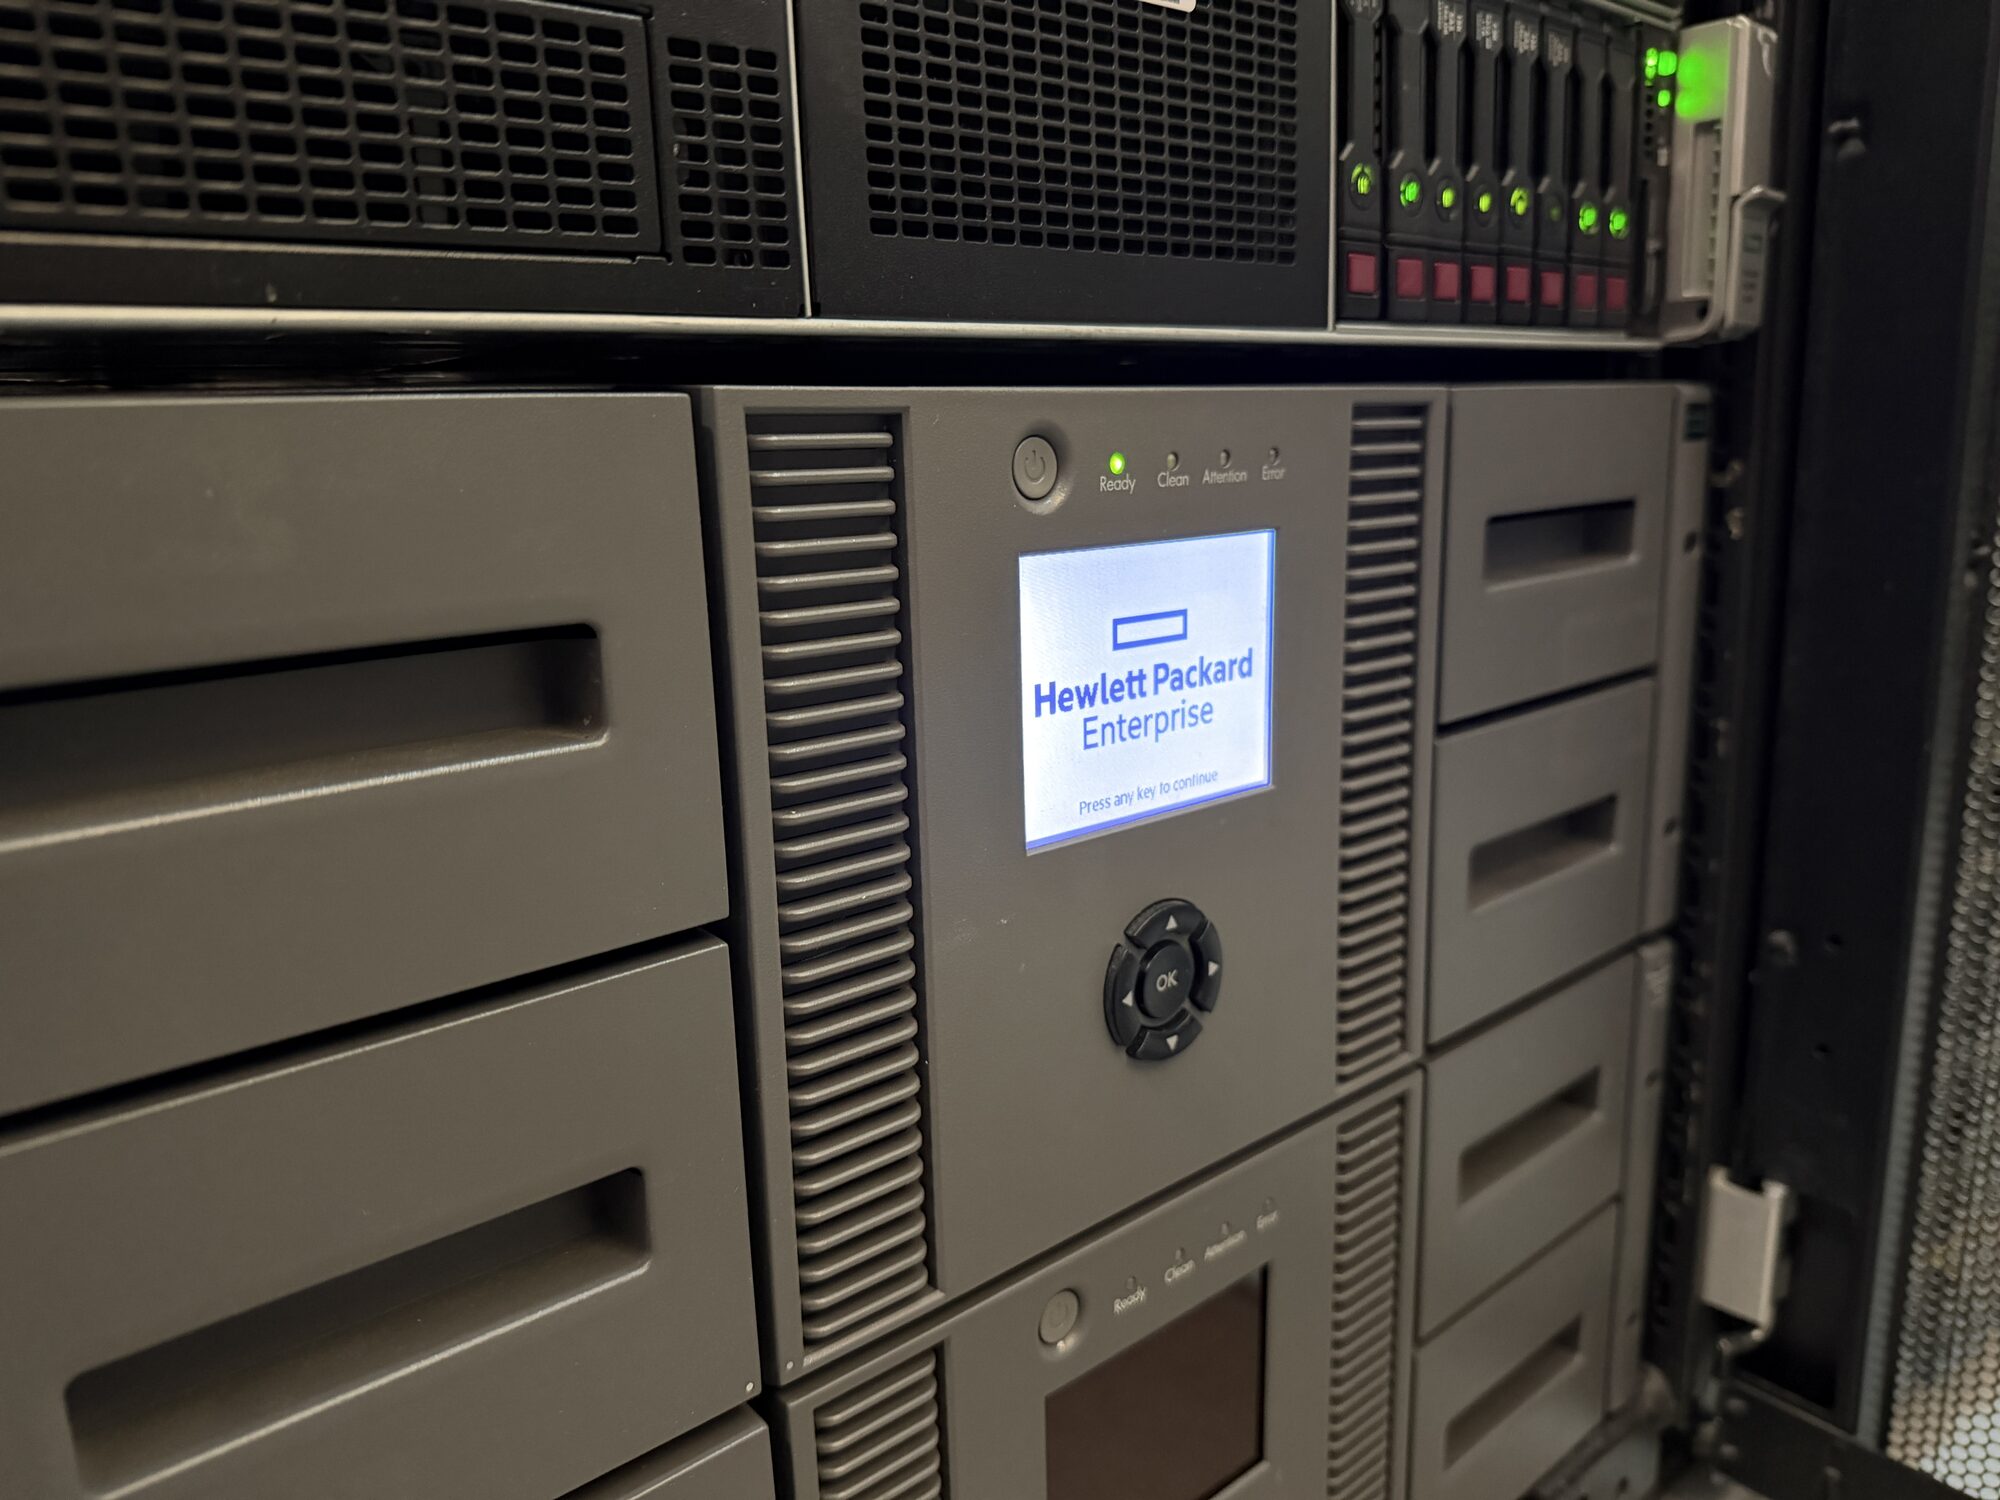
Our backups are designed for the day an intruder is on your server. Our backups are pull-only by design: the backup side reaches in and takes the copy, and production has no path back to it. Encrypted at rest, kept in the EU, and restored on purpose, regularly, so the first restore is never the real one.
What it is
Managed backup for everything we run for you: virtual machines, bare metal Linux and Windows servers, SQL servers, cPanel and Plesk nodes, web roots, configuration and databases. We use two engines, each where it is strongest. Veeam takes image-level backups of virtual machines and agent-based backups of physical servers. Borg, the deduplicating, compressing, encrypting archiver, takes file and database backups from Linux platforms into a dedicated backup hub.
What gets backed up, how often and how long it is kept follows the service you order: a small basic service and a platform with cross-site coverage do not get the same answer, and we write yours down.
How we build it
Pull-only, over the out-of-band network. Backups never travel on the production network. They are taken over our out-of-band management network, which is air-gapped from production: routed, firewalled, and never on the same segment as a production server. The backup systems initiate every transfer. Production servers have no network path to the backup infrastructure and hold no credentials for it. Only our management network may reach the backup hosts; everything else is explicitly denied on the firewall appliances, not just on the hosts themselves.
Veeam for images and agents. Repositories run on XFS with fast cloning, so synthetic full backups cost almost no new space, and a hardened repository tier receives the copy jobs. Larger customers can have a Veeam instance of their own.
Borg for files and databases. The backup hub connects to the customer host, never the reverse, using SSH keys that are locked to a single command and a single set of paths. Files are copied read-only, databases are dumped consistently from a node that is not taking writes, and everything lands in an encrypted, append-only repository with one repository and one passphrase per customer. The key that creates archives cannot delete them; retention is enforced by a separate, local job on the hub.
Coverage checked against reality. We compare what is running against what is fresh on backup disk, not against a job's success status.
Restores tested, as often as weekly. We restore files, databases and whole machines on a schedule, into scratch space, and check the result.
Encrypted at rest by default. EU data stays in the EU. Backups and replicas of EU-hosted data stay inside our EU infrastructure.
What it protects you from
- Ransomware or an intruder deleting the backups from the server it just compromised.
- Gaps in coverage.
- Discovering at restore time that the backup does not restore.
- One customer's backups being readable with another customer's keys.
- Your data leaving the EU because a backup was copied somewhere convenient.
In practice
A digital agency, on its own dedicated Veeam. The agency runs a Veeam backup server of its own, with a scale-out repository spread across several extents on enterprise storage. We operate it end to end, from the jobs to the repositories to the directory integration it depends on.
A news publisher's web roots, backed up in parallel. A news publisher's web root holds millions of small files. Instead of moving them across the network one by one, the backup runs on the source in parallel streams that use the server's idle cores, sends only deduplicated, compressed chunks to the hub, and finishes in a fraction of the time a single stream needed.
One hub, many shapes. The same Borg hub protects a three-node database cluster, dual web nodes with near-identical web roots, and single-server stacks. Each has its own manifest describing what to take and how; the trust model is identical for all of them.
Why EuroVPS
- Pull-only backup, enforced on the firewall, not on a promise.
- Append-only, per-customer encrypted repositories.
- Coverage verified against the live inventory, not job status.
- Restores tested as often as weekly.
- Veeam and Borg run by the engineers who run your platform.
FAQ
Can I back up my own servers to you? Our backups are pulled by our systems from yours. That is the design that keeps a compromised server away from its own backups, and it is the same for every customer.
How quickly can you restore? It depends on the service you order and what is being restored: a single file, a database or a whole machine. We define the restore path for your service up front and test it.
Are my backups encrypted? Yes, at rest by default, and in transit over SSH or the backup engine's own encrypted channel.
Where are my backups kept? Backups of EU-hosted data stay inside our EU infrastructure.
Can I restore a single file from last week? Yes. Both engines restore individual files from any retained point, as well as whole databases and machines.
If you want backups that are still there on the worst day, Talk to an engineer.
Your next infrastructure partner
Let’s look at
your setup.
Tell us what you run today and what needs to improve. An engineer will review your brief and help you plan the next step.
+357 222 32280
who will look after your infrastructure.
Let’s start with your setup.
A little context helps us start the right conversation.