

What we do · Operations
GDPR: your data stays in the EU
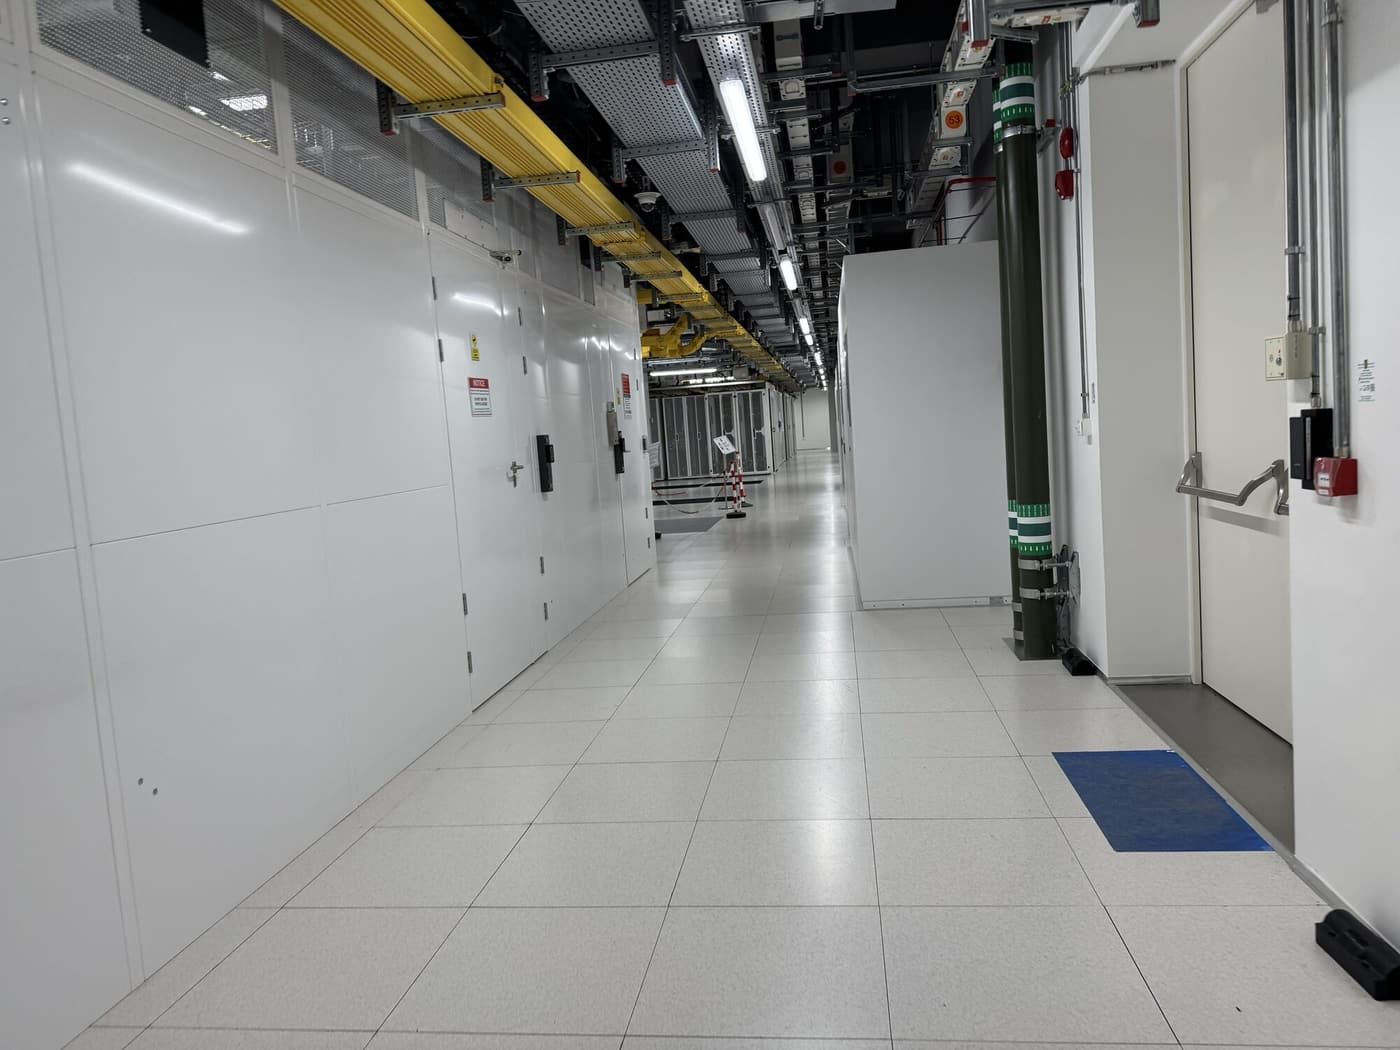
When you host personal data with us in Europe, it stays in Europe, on our own hardware, in our own cages, operated by our own engineers. We sign a Data Processing Agreement with you, and we give you our technical and organisational measures in writing, so your records of processing can point to something real.
What it is
Our GDPR posture is a set of facts about where your data lives and who can touch it, backed by contracts and by certified controls:
- EU locations. Our European datacenters are in Athens, at Digital Realty, and in Amsterdam. Our corporate headquarters is in Cyprus.
- No public cloud underneath. Your data does not sit on a hyperscaler's platform behind our name. The servers, storage arrays, networks and backup systems are ours.
- A Data Processing Agreement. We act as your processor under Article 28 and sign our own DPA with you, setting out what we do with your data, which is only what you instruct us to do.
- Technical and organisational measures in writing. Our Article 32 TOM document describes the security of processing in detail. Request it below.
- Certified management systems. ISO/IEC 27001 with ISO/IEC 27017 and ISO/IEC 27018, the code of practice for protecting personal data in cloud services.
How we build it
Data residency by design. Your platform is built in the datacenter you choose. Storage, replicas and backups of EU-hosted data stay inside our own EU infrastructure. Customers who choose our Toronto site do so deliberately, for data that belongs there.
Our own staff, our own hardware. Hardware in our cages is installed and maintained by our engineers. Our datacenter operators provide power, cooling and physical security under their own certified programmes. They do not access your systems.
Access only where it is needed. Administrative access is by SSH key, through our own VPN gateways and jump hosts, on a management network that customer traffic cannot see.
Backups that attackers cannot reach. Backups are pull-only: the backup side pulls from production and production has no network path to the backup plane at all, enforced on firewall appliances. A compromised server cannot touch, encrypt or delete its own backups.
Encrypted in transit and at rest. Traffic between our datacenters and our corporate headquarters crosses our own encrypted backbone, IPsec with AES-256. Data on storage and in backups is encrypted at rest by default, and retired drives are sanitised with Blancco, with an erasure certificate kept for every disk.
AI that stays local. Where we provide AI processing, such as search over archives or analysis of documents, the models run on GPUs in our own datacenter. Your data is never sent to a public AI service.
What it protects you from
- Personal data quietly replicated outside the EU by a cloud platform.
- Sub-processors you never agreed to.
- A processor who cannot describe its own security in writing.
- Backups that ransomware can reach and destroy.
- Personal data sent to public AI services.
In practice
Medical records, analysed on local AI. A customer needed AI to analyse medical records. We built it inside Digital Realty Athens, on the customer's own private GPUs, so the patient data never left their platform and never touched a public cloud.
A partner's tender, with the paperwork ready. When a digital agency needed assurance for a public-sector tender, our signed statement confirmed that data is stored and processed exclusively in the EU, backed by our certificates and the Digital Realty assurance pack.
Why EuroVPS
- European hosting on our own hardware, not resold public cloud.
- Our own DPA signed with every customer, and an Article 32 TOM document provided.
- ISO/IEC 27018 controls for personal data in cloud services.
- Pull-only backups that production cannot reach.
- AI processing on your own private GPUs, never a public AI service.
FAQ
Where exactly is my data? In the datacenter you chose: Athens or Amsterdam for the EU. Replicas and backups of EU-hosted data stay inside our EU infrastructure.
Will you sign our DPA? We work with our own DPA, the same for every customer, built around the measures in our TOM.
Who are your sub-processors? Our datacenter operators provide the facilities. Ask us for the current list for your service.
Can I have the TOM document? Yes. Request it with the form below and we send it to you.
How would you notify us of a personal data breach? Without undue delay, as Article 33 requires of a processor, with the facts we have and what we are doing about them.
Request our technical and organisational measures, or Talk to an engineer.
Your next infrastructure partner
Let’s look at
your setup.
Tell us what you run today and what needs to improve. An engineer will review your brief and help you plan the next step.
+357 222 32280
who will look after your infrastructure.
Let’s start with your setup.
A little context helps us start the right conversation.